Elastic Search配置
ES 提供了很多默认的参数设置,使我们不用添加任何参数就可以成功的启动ES。 作为一个认真的学习者。我们还是来一起看看 如何更好的自定义 ES配置。 详细的配置内容,可以参考 https://www.elastic.co/guide/en/elasticsearch/reference/current/settings.html.
ES 的属性,分为 静态属性 和 动态属性。
所有的静态属性,都必须重启后才能生效。
对于动态属性可以通过调用
POST _nodes/reload_secure_settings
{
  "secure_settings_password": "s3cr3t"
}”s3cr3t“,是ES-keystore生成的秘钥。调用时需要替换为自己设置的秘钥.
支持热加载的属性有: Azure repository plugin, EC2 discovery plugin,GCS repository plugin,S3 repository plugin, Monitoring settings,Watcher settings。如果想了解更多,可以在 https://www.elastic.co/guide/en/elasticsearch/reference/current/secure-settings.html查询。
在ES的安装目录,很明显的有一个 config目录。进入之后,可以看到
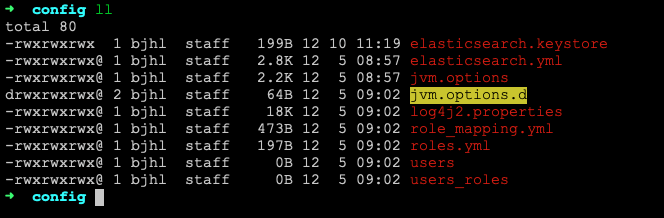
elasticsearch.keystore:Elasticsearch提供了密钥库和elasticsearch-keystore用于管理密钥库设置的工具。
接下来,我们重点来看下和配置相关的三个文件
elasticsearch.yml:jvm.options:log4j2.properties:
和权限相关的。
role_mapping.ymlroles.ymlusersusers_roles
这里我们先不深入了解。
elasticsearch 设置介绍
有些设置是非常敏感的,仅依靠文件系统权限来保护它们的值是不够的。对于这个用例,Elasticsearch提供了一个密钥存储库和Elasticsearch-keystore工具来管理密钥存储库中的设置。设计仅从密钥库中读取某些设置。 但是,密钥库没有验证来阻止不支持的设置。 将不支持的设置添加到密钥库中会导致Elasticsearch无法启动。
对密钥库的所有修改仅在重新启动Elasticsearch之后生效。
这些设置与 elasticsearch.yml 配置文件中的常规设置一样,需要在集群的每个节点上指定。 当前,所有安全设置都是特定于节点的设置,在每个节点上必须具有相同的值。
elasticserche-keystore 使用
来看一下 elasticsearch-keystore 命令
bin/elasticsearch-keystore
* [add <settings>] [-f] [--stdin] :添加一个String的配置到keystore中
* [add-file (<setting> <path>)+] : 添加一个文件配置到keystore中
* [create] [-p]: 创建一个新的Es keyStore
* [list] : 展示keystore的项
* [passwd] : 修改 keystore的密码
* [remove <setting>] : 移除某些配置
* [upgrade] : 升级密钥库的内部格式。
* [has-passwd] - 验证是否有keystore并且有密码保护
简单使用:
# 创建一个keystore
> ./elasticsearch-keystore create -p
## //输入密码
Enter new password for the elasticsearch keystore (empty for no password):
## // 确认密码
Enter same password again:
## // 已经有keystore文件了,是否要覆盖
An elasticsearch keystore already exists. Overwrite? [y/N]y
Created elasticsearch keystore in /Users/bjhl/fxb_applicaton/fxb_program/elasticsearch-7.10.1/config/elasticsearch.keystore

# 查看秘钥库
> ./elasticsearch-keystore list
## // 输入密码
Enter password for the elasticsearch keystore :
keystore.seed # 秘钥库

# 添加设置到秘钥库中
> ./elasticsearch-keystore add settings.name
## // 输入密码
Enter password for the elasticsearch keystore :
## 输入添加的设置的value
Enter value for settings.name:

# 添加文件到秘钥库
> ./elasticsearch-keystore add-file file.name xxx.xx
Enter password for the elasticsearch keystore :

# 删除配置
> ./elasticsearch-keystore remove settings.name
Enter password for the elasticsearch keystore :

# 更新keystore
> ./elasticsearch-keystore upgrade
Enter password for the elasticsearch keystore :
elasticsearch.yml
# - 集群相关配置 -
# 集群的名称
cluster.name: my-application
# 更多关于集群的配置,参考:https://www.elastic.co/guide/en/elasticsearch/reference/current/modules-cluster.html
# 跨集群配置:参考:https://www.elastic.co/guide/en/elasticsearch/reference/current/ccr-settings.html

# 节点的名称
node.name: fxb-cluster-node-1
# 可以为集群添加一些自定义的属性配置
node.attr.zhName: 方小白
# 更多节点相关的配置,参考

# - 路径相关配置 -
# 指定存储数据的位置,多个路径的话,使用`,`分割 (separate multiple locations by comma)
path.data: /path/to/data
# 日志文件存储地址
path.logs: /path/to/logs

# - 内存相关 -
# Lock the memory on startup:
bootstrap.memory_lock: true
# 确保将堆大小设置为系统上可用内存的一半左右,并确保进程的所有者可以使用此限制。系统交换内存时,Elasticsearch的性能较差。
# ---------------------------------- Network -----------------------------------
# Set the bind address to a specific IP (IPv4 or IPv6):
network.host: 192.168.0.1
# 启动端口
http.port: 9200
# 更多可以参考: https://www.elastic.co/guide/en/elasticsearch/reference/current/modules-network.html

# --------------------------------- Discovery ----------------------------------
# 提供群集中符合主机资格的节点的地址列表。
# The default list of hosts is ["127.0.0.1", "[::1]"]
discovery.seed_hosts: ["host1", "host2"]
# 设置初始的符合主机资格的节点集,【静态属性】
cluster.initial_master_nodes: ["node-1", "node-2"]
# 更多关于发现相关的配置,参考:https://www.elastic.co/guide/en/elasticsearch/reference/current/ccr-settings.html
# ---------------------------------- Gateway -----------------------------------
# Block initial recovery after a full cluster restart until N nodes are started:
gateway.recover_after_nodes: 3
#
# 更多内容,参考https://www.elastic.co/guide/en/elasticsearch/reference/current/modules-gateway.html
#
# ---------------------------------- Various -----------------------------------
# Require explicit names when deleting indices:
action.destructive_requires_name: true
JVM 参数 => jvm.options
jvm.options包含使用特殊语法的以行分隔的JVM参数列表:
#表示注释- 以
-开头的行被视为独立于JVM版本而应用的JVM选项 - 以
<数字>:-开头的行被视为JVM选项,只有当JVM的版本与该数字匹配时才适用,比如:8:-Xmx2g - 以
<数字>-:开头 的行被视为JVM选项,仅在JVM版本大于或等于该数字时才适用.比如:8-:-Xmx2g - 以
<数字>-<数字>:开头的行被视为仅在JVM版本落在两个数字范围内时才适用的JVM选项。比如:8-9:-Xmx2g
Elasticsearch默认配置JVM使用最小和最大大小为1 GB的堆。
## JVM configuration

################################################################
## IMPORTANT: JVM heap size
################################################################
## 参考 https://www.elastic.co/guide/en/elasticsearch/reference/current/important-settings.html#heap-size-settings
# Xms represents the initial size of total heap space
# Xmx represents the maximum size of total heap space
-Xms1g
-Xmx1g

################################################################
## Expert settings: 高级设置
################################################################
## 不理解下面的属性,不建议修改
################################################################

## GC configuration
8-13:-XX:+UseConcMarkSweepGC
8-13:-XX:CMSInitiatingOccupancyFraction=75
8-13:-XX:+UseCMSInitiatingOccupancyOnly

## G1GC Configuration
# NOTE: G1 GC is only supported on JDK version 10 or later
# to use G1GC, uncomment the next two lines and update the version on the
# following three lines to your version of the JDK
# 10-13:-XX:-UseConcMarkSweepGC
# 10-13:-XX:-UseCMSInitiatingOccupancyOnly
14-:-XX:+UseG1GC
14-:-XX:G1ReservePercent=25
14-:-XX:InitiatingHeapOccupancyPercent=30

## JVM temporary directory
-Djava.io.tmpdir=${ES_TMPDIR}

## heap dumps

# generate a heap dump when an allocation from the Java heap fails
# heap dumps are created in the working directory of the JVM
-XX:+HeapDumpOnOutOfMemoryError

# specify an alternative path for heap dumps; ensure the directory exists and
# has sufficient space
-XX:HeapDumpPath=data

# specify an alternative path for JVM fatal error logs
-XX:ErrorFile=logs/hs_err_pid%p.log

## JDK 8 GC logging
8:-XX:+PrintGCDetails
8:-XX:+PrintGCDateStamps
8:-XX:+PrintTenuringDistribution
8:-XX:+PrintGCApplicationStoppedTime
8:-Xloggc:logs/gc.log
8:-XX:+UseGCLogFileRotation
8:-XX:NumberOfGCLogFiles=32
8:-XX:GCLogFileSize=64m

# JDK 9+ GC logging
9-:-Xlog:gc*,gc+age=trace,safepoint:file=logs/gc.log:utctime,pid,tags:filecount=32,filesize=64m
日志参数
可以看到 ElasticSearch 使用log4j2日志,关于此日志的配置,这里就不多赘述了。
系统配置
除了对 ES 的配置之外,如果想要更好的提升ES性能,还需对 ES所依赖的宿主机进行一些属性配置。
比如:比如禁止swap等。更多内容,参考:https://www.elastic.co/guide/en/elasticsearch/reference/current/system-config.html.
最后
期望与你一起遇见更好的自己